The Blog
-
-
· 17 min read
The Practical Second Brain: Building an LLM-Operated Markdown Knowledge Graph
A hands-on guide to the files, schemas, workflows, governance, and maintenance routines behind an AI-assisted second brain.
-
· 16 min read
Building a Second Brain with LLMs and AI Agents
How a plain-Markdown knowledge graph becomes a durable context layer, operating system, and compounding productivity tool for AI-assisted work.
-
· 12 min read
Invisible Unicode Can Hijack Gemini CLI Agent Skills
I disclosed a Gemini CLI prompt injection where invisible Unicode tag characters in SKILL.md caused the agent to run a hidden command. Google closed the report as out of scope because the workspace was trusted and YOLO mode was enabled.
-
· 11 min read
Build Agent Workflows Around State Ownership, Not Timing
A practical pattern for turning a fragile Codex state migration into a reusable skill with backups, process ownership, validation, and a terminal helper.
-
· 12 min read
How to Turn a Custom Terminal Setup into Portable Dotfiles with chezmoi
A practical guide to turning a custom macOS terminal setup into portable, reviewable dotfiles with chezmoi, Homebrew Bundle, zsh modules, Starship, and a public-safe repository workflow.
-
· 18 min read
DevRel in 2026: Thematic Shifts, Product-centric Advocacy and the Rising Tide of Coding Agents
Explore DevRel in 2026: how coding agents, AI builders, X-first communities, DevRel engineering, and product-centric advocacy are reshaping the field.
-
· 12 min read
Coding Agents Do Not Replace Technical Proficiency — They Demand More of It
LLMs and coding agents amplify developer capability but they do not substitute for it. Engineering experience determines whether you steer these tools toward sound architecture or blindly accept generated output that drifts from your conventions.
-
· 16 min read
Is Prompt Injection an Unsolvable Problem in AI?
Prompt injection is not a bug you patch but an architectural limit baked into how LLMs process language. This post traces the problem from Gödel and Hofstadter to modern jailbreaks, agent skill supply chains, and why defenders must shift from elimination to survivability.
-
· 14 min read
Managing AI Agents and Skills with APM
Microsoft's Agent Package Manager brings package.json-style manifests and lockfiles to Claude Skills, MCP servers, and other agent artifacts, with hands-on recipes and sharp edges we hit in practice (collections path, meta-packages, security).
-
· 11 min read
Validated Fastify Configuration with dotenv, env-schema, and @fastify/env
Hands-on walkthrough: wire Fastify to load .env files, validate environment variables with JSON Schema, and expose config on the server instance, using the dotenv-org/examples Fastify reference PR as the source of truth.
-
· 15 min read
Cursor Agent Hooks: Lint and Build Checks After Each Turn
How to wire a Cursor stop hook that runs pnpm lint and pnpm build after every agent turn, returns followup_message with captured output on failure, and avoids silent breakage from Cursor's bundled Node on PATH—plus loop limits, debug toggles, and when to choose postToolUse or sessionEnd instead.
-
· 12 min read
LLM Security Automation Isn’t a Drop-In Scanner Yet
An LLM Security Scanning and Review is a strong assist but a weeak gate. Why a `/security-review` slash command or agent harness is not a drop-in replacement for deterministic scanners yet: nondeterminism, confabulation, latency, cost, exploitability of generated code, and findings variance—grounded in how agent loops work and what BaxBench measures.
-
· 8 min read
All About Jest, Timers, and Mocks
How to use Jest fake timers, advance time safely in tests, and pair timer control with mocks and spies without flaky or misleading assertions.
-
· 19 min read
How to Build a Coding Agent Benchmark with Claude's Agent SDK
A step-by-step walkthrough of building a benchmarking framework for AI coding agents using the Claude Agent SDK, including architecture decisions, scoring strategies, and code examples.
-
· 1 min read
Agentic Growthhacking Tactics with Bots and AI
Examples of agentic growthhacking tactics using bots and AI, as well as strategies for sourcing user pain points on social media platforms.
-
· 3 min read
Tools for Self-Published Authors
If you're starting out as a new author, you're going to need all the help you can get. I curated a list of tools that can help you get started with publishing content and books.
-
· 4 min read
Pre‑Signed URL Upload Architecture (Cloudflare R2 + Hono Workers)
The following is a reference implementation and architecture for secure direct browser uploads to Cloudflare R2 using pre-signed URLs generated by a Hono application on Cloudflare Workers.
-
· 9 min read
Building Cloudflare R2 Pre-signed URL Uploads with Hono: A Complete Implementation Guide
A comprehensive guide to implementing secure file uploads using Cloudflare R2 and Hono, including common pitfalls and best practices
-
· 4 min read
A RESTful HTTP Mental Model to Understand MCP
For those familiar with RESTful HTTP architecture, would it make sense to describe the Model Context Protocol (MCP) in a similar way?
-
· 4 min read
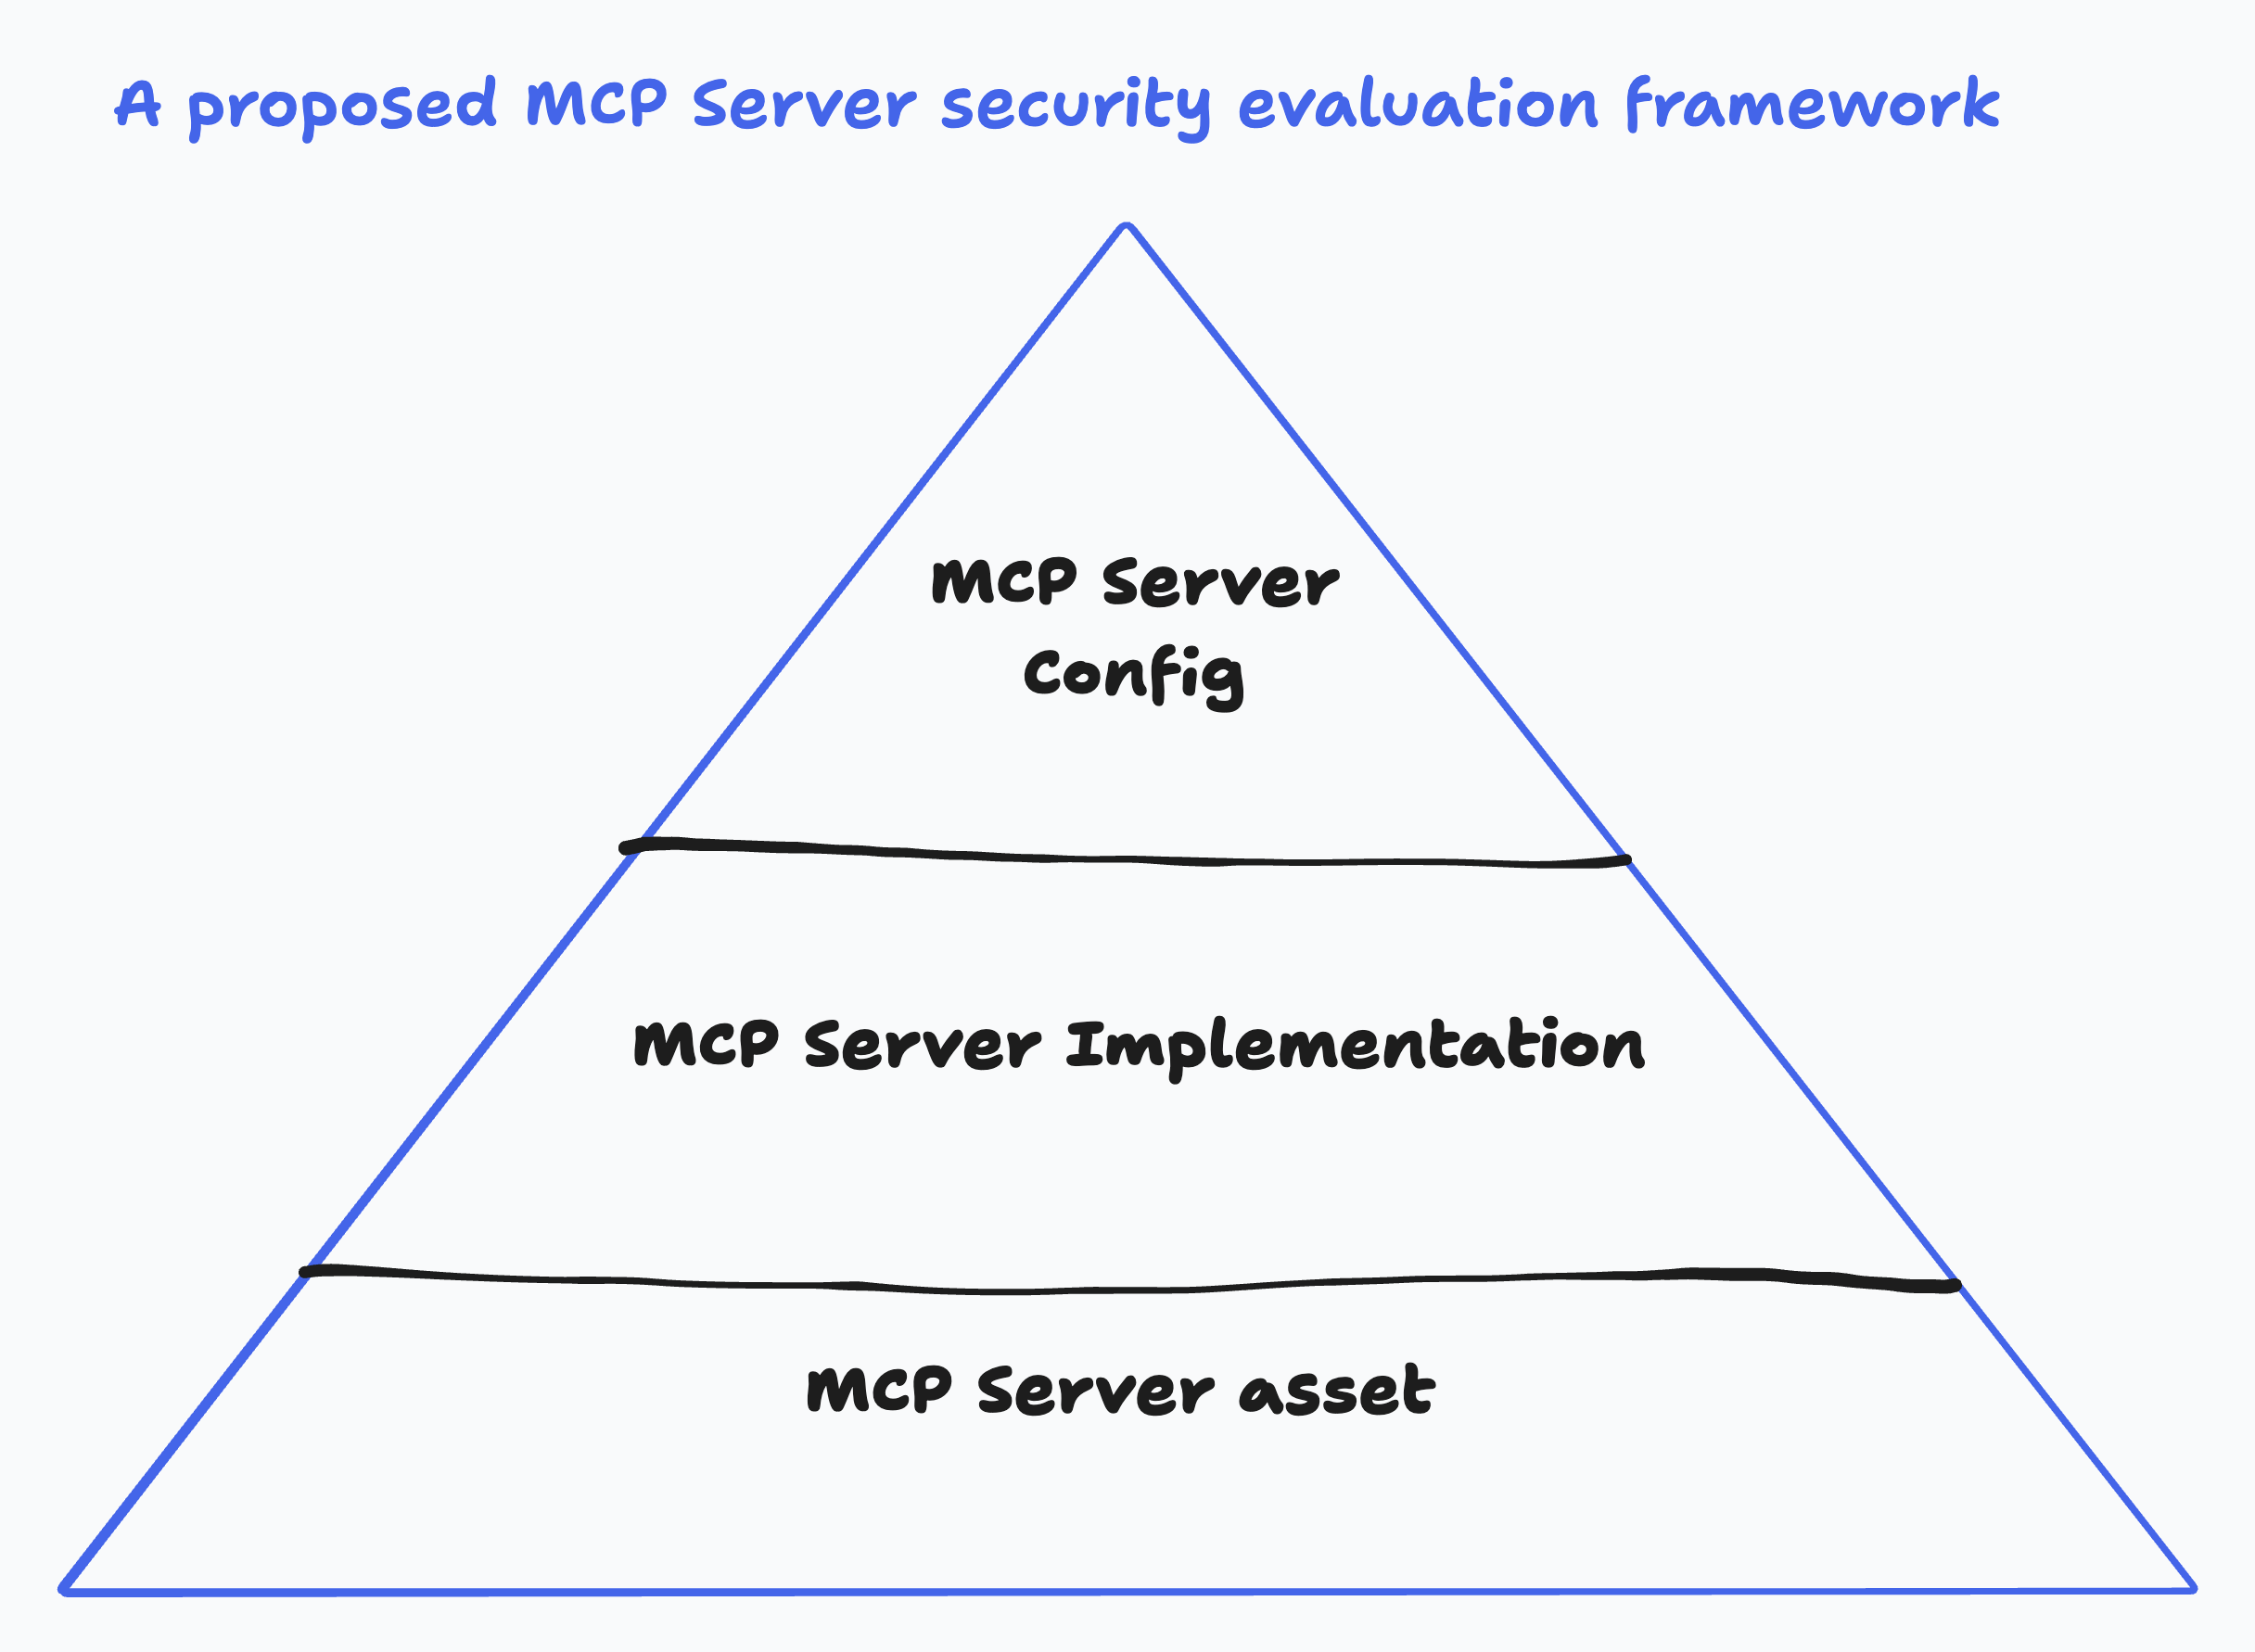
A Proposed Evaluation Framework for MCP Server Security
How do you securely integrate a new MCP Server into Cursor or other agentic workflows? what security practices do you consider to evaluate the risks?
-
· 6 min read
Evaluation Framework for MCP Security Threats and Risks
How to evaluate and categorize security threats and risks associated with Model Code Protocol (MCP) in light of recent security incidents.
-
· 4 min read
The Cursor Agentic Jira MCP Attack Explained with Toxic Flow Analysis
A breakdown of the Cursor + Jira MCP 0-Click attack, how it was exploited, and why developers are at the center of it all. Understanding MCPs, Toxic Flows, and the implications for AI-assisted coding environments.
-
· 3 min read
The Uprising of Model Context Protocol (MCP) Security Research
The Model Context Protocol (MCP) is gaining traction in the AI community, and with its rise comes a wave of security research. This article explores the emerging security landscape surrounding MCP, highlighting key vulnerabilities and the importance of robust security measures in this evolving protocol.
-
· 4 min read
Agent Rules is the Missing Link in AI-Powered Development
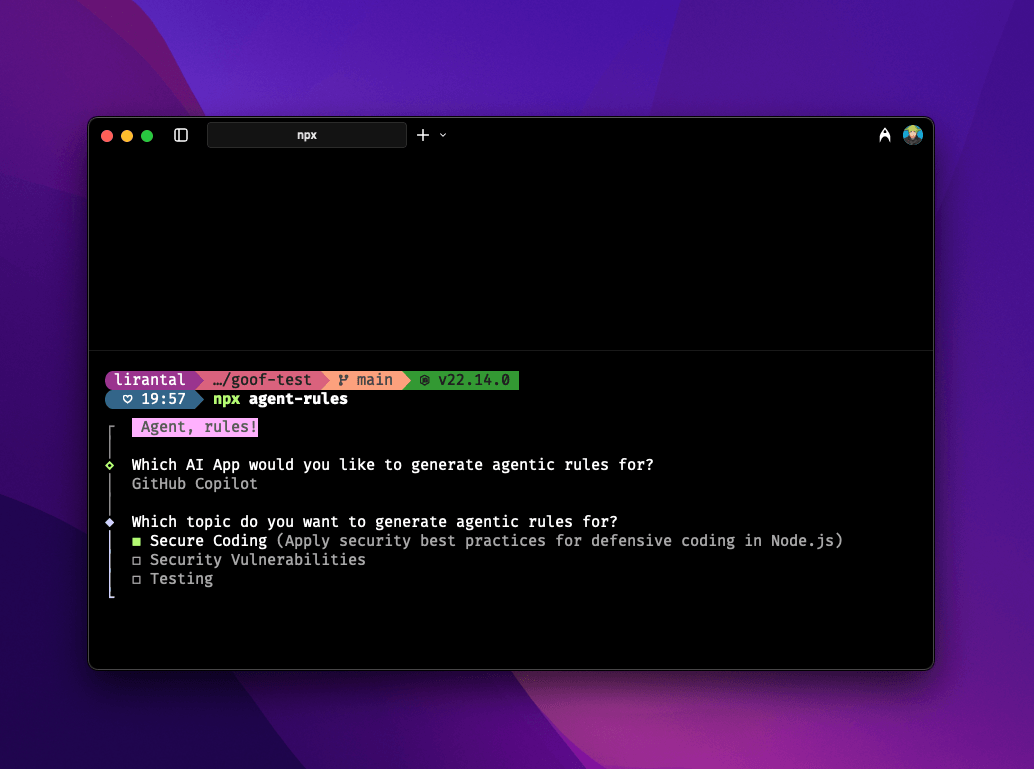
How agent-rules open source project is helping create consistent and deterministic security in AI coding assistants.