Supply chain security
lockfile-lint
Lint lockfiles for trusted registries and protect against lockfile injection.
Security researcher Author Open-source maintainer
I research emerging threats and build open-source defenses for AI agents, the software they write, and the tools they trust.
I head Developer Relations at Snyk
Supply chain security
Lint lockfiles for trusted registries and protect against lockfile injection.
Developer tooling
Check package health and security signals before installing npm dependencies.
Community guide
A practical guide to building thoughtful, accessible, and reliable command-line applications.
From the terminal to the stage.
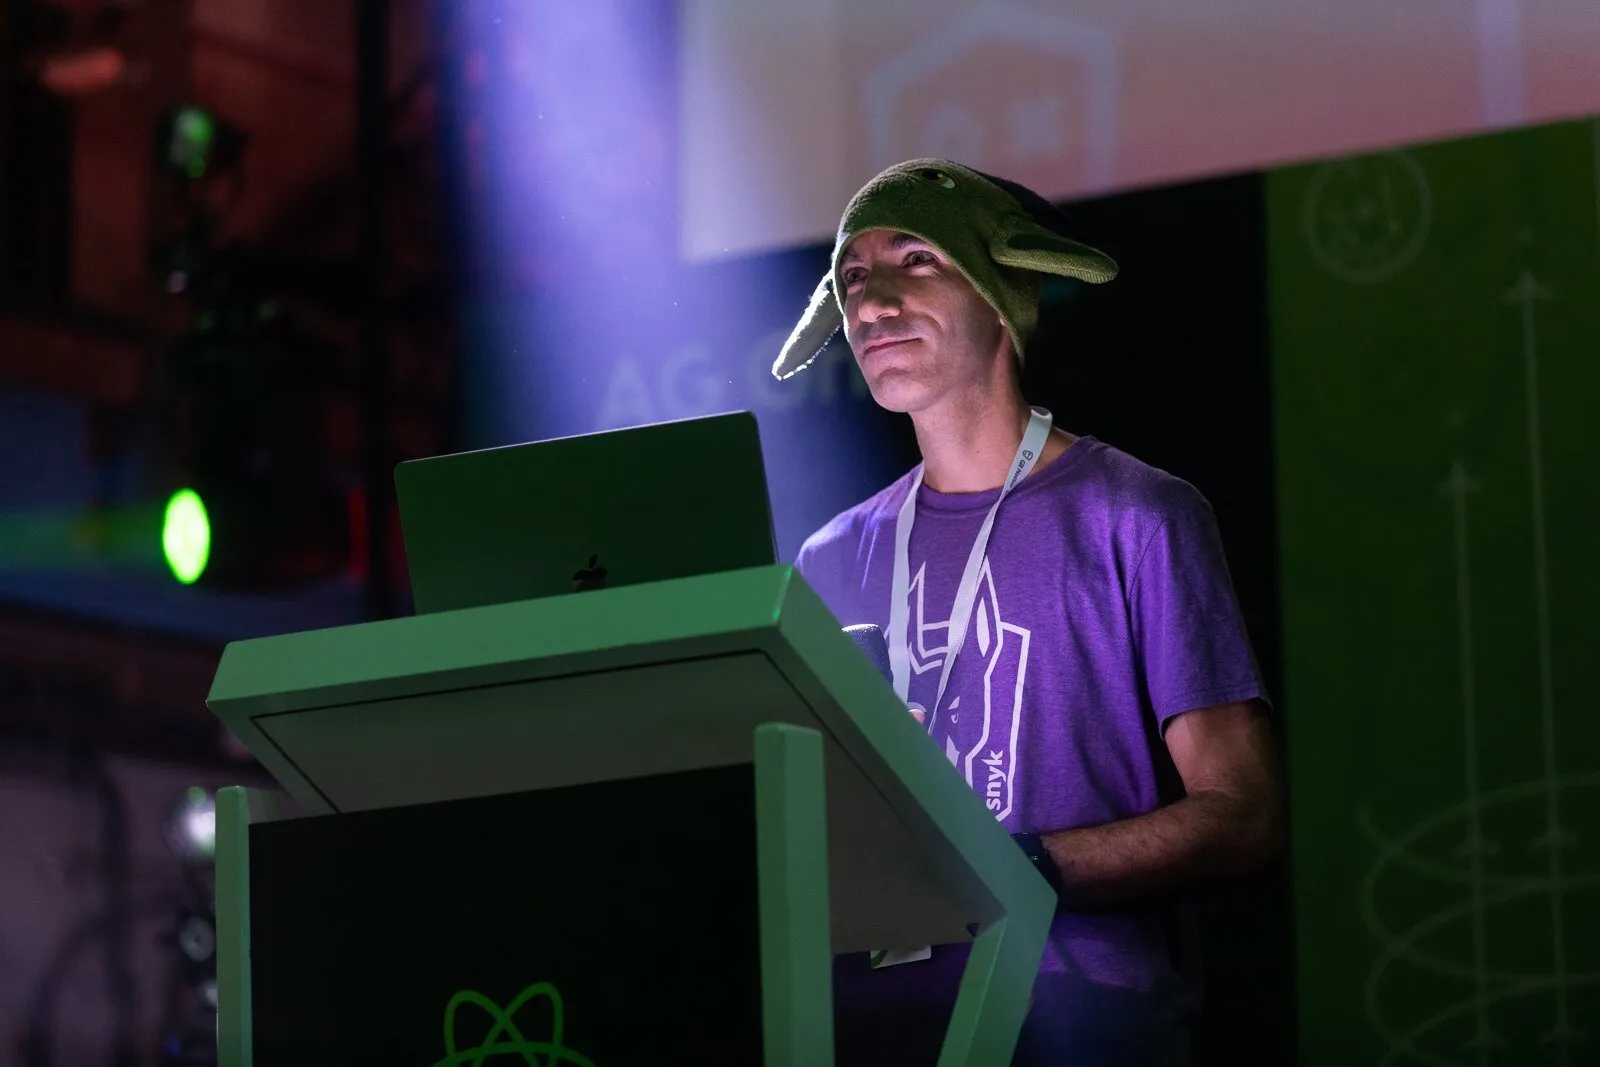
223 talks. 21 countries.
Plenty of live hacking.
I bring real-world attacks and practical defenses to conferences, meetups, and workshops. AI security, Node.js, and the software supply chain, explained through code.
What I’m learning. What I’m sharing.
On the blog ·
Build a private, mobile-first Hermes Agent using Matrix Synapse, Element, end-to-end encryption, Tailscale Serve, and separate Proxmox LXC containers.
On the blog ·
A hands-on guide to the files, schemas, workflows, governance, and maintenance routines behind an AI-assisted second brain.
On the blog ·
How a plain-Markdown knowledge graph becomes a durable context layer, operating system, and compounding productivity tool for AI-assisted work.
Investigating how systems fail.
My work spans AI agents, developer tooling, and software supply chain security: co-authored papers, vulnerability disclosures, patents, and research that became practical defenses.
October 2026
arXiv · Preprint
A benchmark of 307 dependency upgrades across 43 repositories, evaluating whether AI agents fix vulnerabilities while preserving successful builds and tests.
Gabija Pasiunaite, Ryan McMorrow, Brian Clark, Liran Tal, and Luke Tu
June 2026
arXiv · Preprint
Repeated vulnerability scans on JavaScript code explore the consistency of LLM security review and how it complements deterministic static analysis.
Liran Tal, Johannes Kloos, Arsenii Rudich, Stephen Thoemmes, and Manoj Nair
Useful tools. Shared with everyone.
5 selected maintained packages
6 featured repositories
6 featured repositories
Sep 17, 2026 – Oct 16, 2026. Package downloads, not unique developers; totals include dependency installs.
GitHub snapshot: Oct 20, 2026. Stars and forks across the six featured repositories, not unique people or all my projects.
Supply chain security
Lint lockfiles for trusted registries and protect against lockfile injection.
Developer tooling
Check package health and security signals before installing npm dependencies.
Developer tooling
An interactive terminal interface for managing Docker containers and services.
Code security
Detect bidirectional Unicode characters used to disguise malicious source code.
Community guide
A practical guide to building thoughtful, accessible, and reliable command-line applications.
Curated resources
Security resources, tools, and learning material for the Node.js ecosystem.
A bookshelf for more secure code.
Practical guides built around real vulnerabilities, with code to break, fixes to understand, and techniques to take back to your own projects.
Node.js Secure Coding
Node.js Secure Coding
Node.js Secure Coding
Practical web security
Co-author · O’Reilly
From the community
“Some people talk about AppSec (me) and some people really dig in and do the work (you). I’m a big fan.”
“FANTASTIC WORKSHOP! Learned a ton! Thanks a lot 🙏”
“This has become my primary source for learning docker with node. Thanks for sharing these 💝”
“This is one of the best guides I’ve seen on this topic, really cool stuff.”